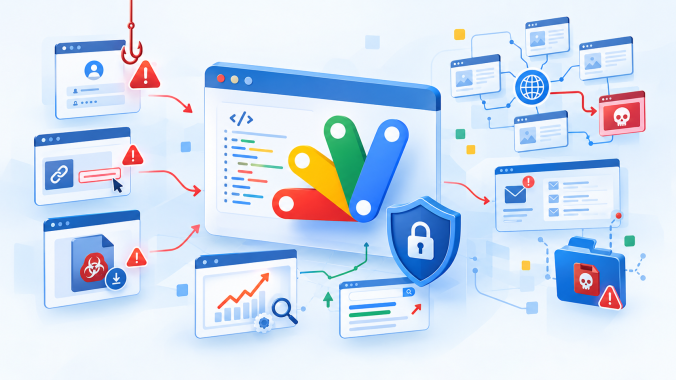

TraceX Labs has published a threat intelligence report examining how Google Apps Script Web Apps are being misused in phishing, fraud, malware distribution, search manipulation, spam and malicious redirection. Released on September 30, 2026, as report GLOBAL-026, it assigns the overall threat a “high” assessment. The report stresses that Google Apps Script remains a legitimate cloud platform and that the misuse of its infrastructure does not imply that Google created, endorsed or controls the associated content.
Apps Script Web Apps can receive HTTP requests, process parameters, generate web pages and communicate with external resources. According to TraceX Labs, threat actors can abuse those capabilities to host intermediate pages or redirects that lead victims to phishing sites, fraudulent offers or malware downloads. Documented schemes include credential theft, investment and employment scams, impersonation, fake payment activity and social engineering, as well as the distribution of suspicious Android APK files.
A major focus of the report is search-engine manipulation. TraceX Labs identifies keyword-heavy landing pages, doorway pages, automatically generated content, unrelated keywords, repeated templates, excessive outbound links and redirect chains as potential warning signs. It maps deliberate search-visibility manipulation to MITRE ATT&CK technique T1608.006, “SEO Poisoning,” while also examining backlink abuse, Google search spam and video-search spam.
The research additionally covers gambling and betting spam, drug-related spam, movie-piracy searches, adult and “not safe for work” content, and deepfake or synthetic-media spam. TraceX Labs cautions that keywords, screenshots or a Google-hosted URL alone cannot establish criminality. Investigators must assess the surrounding content, behavior, destinations and relationships within the wider campaign before classifying an activity.
Non-consensual intimate imagery and sextortion are treated as separate, highly sensitive categories requiring careful evidence handling. Suspected CSAM/CSE-related infrastructure is classified as “Suspected / Corroboration Required,” rather than as a confirmed finding. Researchers are advised not to download, reproduce or redistribute sensitive or suspected illegal material unnecessarily and to use redacted evidence in public reports.
The report also cautions that a Google-owned address does not prove a site is safe or endorsed by Google. HTTPS protects data in transit but does not establish that the underlying content is legitimate. TraceX Labs uses classifications including Observed, Correlated, Suspected, Potential, Benign and Unknown, and says infrastructure association does not prove ownership, criminal intent or attribution to Google.
Security teams are advised to combine URL, network and endpoint evidence. Analysts should inspect unusual parameters, deployment identifiers, destination domains, IP addresses, autonomous system numbers, certificates, file hashes, complete redirect chains and downloaded files. The recommended investigation process is to discover, validate, correlate, classify and report suspicious indicators rather than judging them in isolation.
Original Source: https://www.sikkimexpress.com/news-details/tracex-labs-report-examines-google-apps-script-abuse-across-phishing-malware-seo-spam-and-csam-related-infrastructure
Category:
Tags:
Publish Date: