The Deepfake Deluge Is Here: Why Political AI Ads Need a Consent Standard

Deepfakes Are Not Just a Content Problem. They’re a Trust Architecture Problem.
A voter does not need to believe every fabricated video for it to do damage. They only need to hesitate long enough to question what is real.
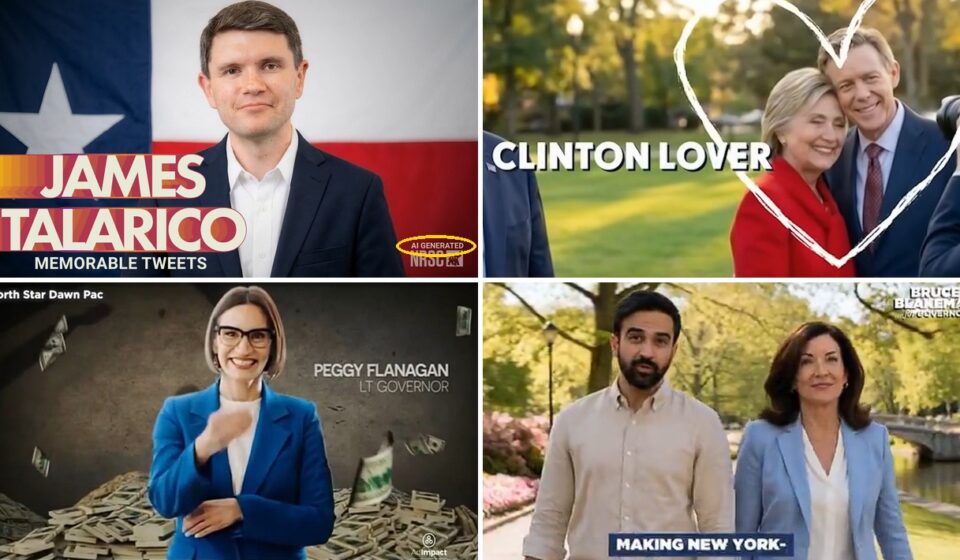
That is the deeper concern as AI-generated political advertising moves from novelty to campaign infrastructure. Reports from the 2026 US midterms describe more than $137 million in spending on AI-made ads, including realistic portrayals of candidates saying or doing things they did not. Research cited in the coverage suggests that people are poor at identifying deepfakes-and that disclosure labels are often missed.
Detection cannot be the whole defence
The instinctive response is to build better detectors. That work matters, but it cannot carry the full burden. Detection systems are probabilistic, models evolve, and content can be altered faster than institutions can update their safeguards. Treating a detector as a final authority risks creating a new failure point: a false sense of certainty.
The architectural question is broader: how do we preserve trust when the media itself can no longer be assumed to be authentic?
For organisations deploying generative AI, this is a familiar challenge. We cannot govern a system only at the point where its output appears. We need controls across the lifecycle: who can generate content, what permissions apply, how outputs are disclosed, where they are distributed, and what evidence remains when a dispute arises.
Political advertising offers a particularly clear test because paid ads pass through identifiable campaigns, platforms and broadcasters. That creates points where accountability can be designed into the process-not just added after a misleading video has already travelled.
Build around accountability, not just labels
A disclaimer is useful only if people notice it, understand it and can trust it. A faint label in a corner is not a meaningful safeguard. Nor is a label alone enough to distinguish harmless creative use from a synthetic portrayal that could mislead viewers.
A more robust approach combines several controls:
- Clear, consistent disclosure: Use plain language, visible placement and, where appropriate, spoken disclosure. “AI-generated” is more immediately understandable than technical or legal phrasing.
- Consent and representation rules: Ask whether the person shown agreed to be represented in that way. This can be a more practical test than trying to define every form of “deceptive” content.
- Provenance and audit trails: Preserve information about how content was produced, edited and approved. Provenance will not prevent every abuse, but it can support accountability.
- Distribution-stage checks: Put obligations where content is paid for and reviewed, while recognising that satire, personal expression and private communication raise different issues.
- Independent evaluation: Test rules against real viewing conditions. A disclosure that works in a policy document but goes unnoticed on a phone screen is not an effective control.
For CTOs and policymakers alike, the trade-off is between friction and resilience. Stronger review processes can slow publishing; weak ones can shift the cost to citizens, who are left to judge synthetic media without reliable tools. The aim should not be to prohibit creative uses of AI. It should be to make consequential, paid communications accountable.
A lesson for India’s information infrastructure
This has a direct relevance to India, where elections, public services and civic debate increasingly depend on digital channels-and where content moves across many languages and communities. A single disclosure standard may not be enough if the wording, voice or format is inaccessible to the audience receiving it.
That makes AI governance an infrastructure question as much as a legal one. Standards should account for local languages, low-bandwidth distribution and the realities of last-mile media consumption. The same principle applies to Digital Public Infrastructure: trust is not created by scale alone. It depends on clear rules, verifiable processes and safeguards that people can actually understand.
The strategic takeaway is simple: do not make citizens the last line of defence against synthetic media. Build accountability into creation, approval and distribution-and treat trust as a system property, not a label.
The next generation of AI governance will be judged not by how convincingly machines can create, but by how responsibly society can verify and use what they produce.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.