The Credibility Gap: When AI Leaders Warn Against Their Own Technology

AI’s Hardest Test Is Not Capability. It Is Credibility
We tend to measure AI by what it can generate, automate, or predict. Yet enterprises and society must increasingly measure it by something less convenient: whether they can trust the context into which it is placed.
A model that suggests a marketing headline represents one category of risk. A model that influences hiring, credit, healthcare, public benefits, or critical infrastructure creates an entirely different system-design responsibility. The technology may be similar; the consequences are not.
The Signal Beneath the Satire
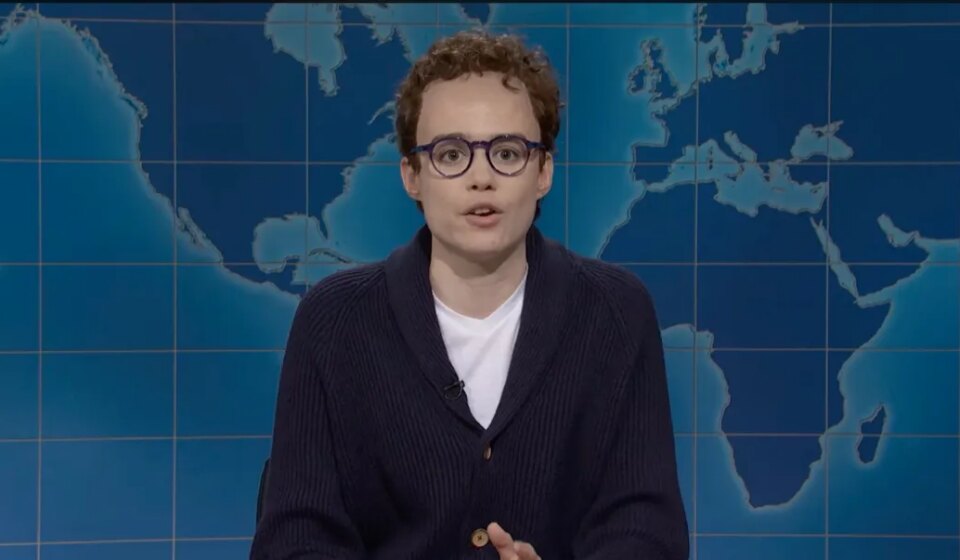
Saturday Night Live recently used Jane Wickline’s fictional portrayal of Anthropic CEO Dario Amodei to highlight a genuine contradiction: AI leaders are simultaneously claiming extraordinary benefits and warning of potentially catastrophic risks.
The segment was comedy, but the underlying trust problem is serious. Society is being asked to support rapid deployment while major institutions still struggle to define who is accountable when increasingly autonomous systems fail.
From Model Risk to System Risk
Most AI discussions remain focused at the model level: accuracy, bias, hallucination, and benchmark performance. These matter, but production AI is a socio-technical system.
Retrieval pipelines, prompts, connected tools, user permissions, business rules, and workflow design can turn an imperfect model into a consequential one. A model with 95% accuracy is not necessarily “95% safe” when its output can authorize a payment, influence a medical decision, or trigger a security action.
My concern is that the central enterprise risk involves automation bias alongside the risk of a bad answer: the human tendency to defer to a machine because it is fast, fluent, and institutionally endorsed.
Architecture must address this through risk-tiered autonomy, least-privilege access, auditable data provenance, independent testing, continuous monitoring, and rapid rollback. A “human in the loop” is not enough if the human lacks the time, information, or authority to challenge the system.
Governance Must Become Executable
A principles document cannot govern an autonomous workflow. Policies must become technical controls that define:
- Which models are permitted for which decisions
- What data each system can access
- Which actions require human approval
- How model and data drift will be detected
- What happens when confidence falls below an acceptable threshold
- How quickly the system can be disabled or reversed
Data sovereignty also requires more than knowing where the database resides. Enterprises must understand where prompts, embeddings, telemetry, and fine-tuning artifacts are stored, processed, and transferred.
For CTOs, AI gateways, evaluation pipelines, policy enforcement, observability, and incident management should be treated as core architectural capabilities-not optional governance overlays. High-risk systems should begin in advisory or shadow mode, operate within narrow boundaries, and gain autonomy only after measurable evidence supports it.
This is not an argument for timidity. It is an argument for staged ambition: move quickly in low-risk areas, but deliberately where errors can become irreversible.
Boards should also ask a more consequential question than “Do we have an AI strategy?” They should ask: What are we allowing this system to decide, who can stop it, and how will we know when it becomes unsafe? A strategy without explicit risk appetite, ownership, and escalation paths is experimentation with enterprise liability.
Relevance for Scaled Digital Systems
In India’s digital public infrastructure and AI-enabled public services, this distinction is especially important. Scale can make governance affordable, but it can also magnify exclusion.
Citizen-facing systems need accessibility across languages and abilities, appropriate explanations, data minimisation, and practical mechanisms for appeal. Otherwise, efficiency gains may simply institutionalise opaque decisions at national scale.
What Leaders Should Do Now
Classify AI use cases by consequence, not model size. Build evaluation and rollback into delivery from day one. Assign business owners who can override the system-not only technical owners. And communicate both capability and limitations without hiding behind either hype or doom.
The deepest lesson from the satire is not that AI leaders sound unusual. It is that technology has advanced faster than institutional maturity. The winners will not merely build capable models; they will build systems worthy of public trust.
The future of AI will be defined less by what machines can do alone than by the quality of the human institutions that design, constrain, and correct them.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.