Architecting Trust: Human Access, AI Systems, and the Binance Breach

The Job Interview That Cost $6 Billion
The most expensive credential in cybersecurity this month wasn’t a private key. It was a calendar invite.
The Signal
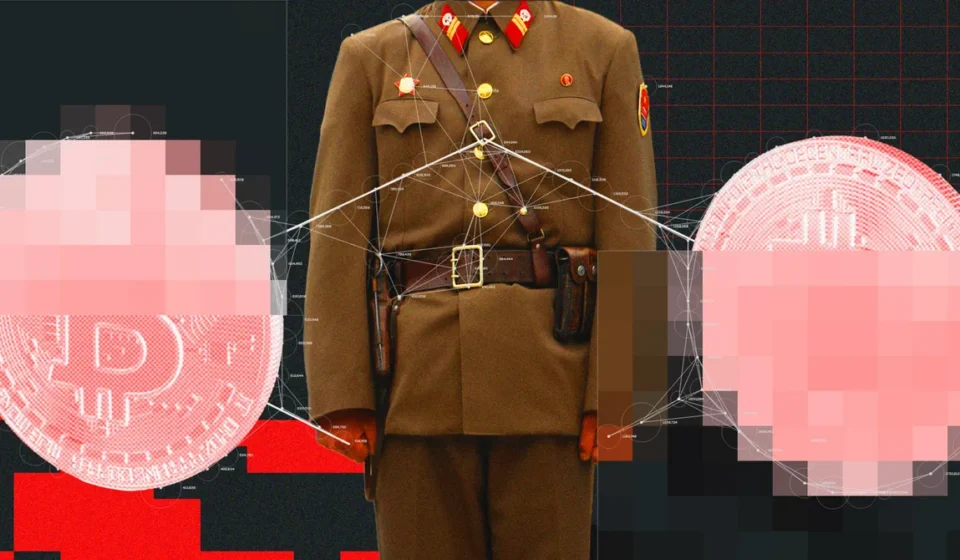
Binance has disclosed how attackers spent months positioning themselves before draining roughly $6.34 billion across more than ten blockchains in about twenty minutes. The entry point: an engineer downloading malware during a fake job interview. From there, the intruders moved laterally, abused an internal AI tool, and reached a wallet-signing service – the one component in the stack that should have been unreachable. The FBI attributed the campaign to DPRK’s TraderTraitor group.
The Architecture Nobody Audits
I have sat through enough enterprise risk reviews to know the pattern. We secure the perimeter, we patch the edge, we buy the SIEM – and then we quietly hand a signing authority to a service account that sits one hop away from a developer’s browser.
Three things in this incident deserve every CTO’s attention.
First, the human layer is a protocol, not a training video. A fake recruiter is not a phishing email you can blocklist. It is a socially engineered payload delivered through a legitimate human aspiration – a better job. Zero Trust was never about network segments; it is the discipline of ensuring a compromised laptop never becomes a trusted principal. Lateral movement is only possible when we let it be.
Second, we have onboarded a new class of insider: the AI agent. Every enterprise deploying internal copilots and retrieval systems is creating non-human identities with broad read access and almost no behavioural baseline. The source reporting doesn’t detail which tool was exploited, but the principle is universal – an internal AI assistant with unscoped permissions and outbound connectivity is a privilege escalation path wearing a productivity badge. Sandbox it, scope it, log every call.
Third, signing authority must be architecturally boring. High-value transaction systems need hardware roots of trust, quorum-based approvals, out-of-band human confirmation, velocity limits, and circuit breakers that trip on anomaly – not policy documents. Twenty minutes is not just a security failure; it is a design failure. No rail should permit that volume to move without multiple deliberate, independent human decisions.
Where Friction Is a Feature
Some in the industry will read this and argue for more automation, faster settlement, fewer approvals. I’d argue the opposite. In high-value systems, friction is a feature – the trick is placing it precisely where the money is, not everywhere. Over-friction creates workarounds; zero-friction creates headlines.
The genuinely hopeful signal here is that nearly half the funds were frozen by a coordinated response across exchanges and tracing firms. That is a distributed immune system – and it works only because the industry shares telemetry faster than it protects turf. Most enterprises still cannot say the same internally.
The Bharat Lens
I have often argued in STPI review meetings that India’s digital public infrastructure succeeds because trust is the actual product – UPI scale is meaningless without settlement certainty. Our transaction rails already embed velocity limits and multi-approval patterns that Western “move fast” crypto stacks rediscovered painfully. That is a design pattern worth exporting, not just admiring.
Closer to home, the emerging founders of the Northeast – building fintech, agri-tech, and DPI-adjacent products in Guwahati and Shillong – are exactly the profile attackers now favour: ambitious, remote-first, hiring fast, and treating security as a post-revenue line item. A fake “client interview” or an unsolicited “vendor RFP” is all it takes. My advice to every young team I mentor: budget for security before you budget for branding.
Takeaways
- Assume breach at the endpoint; never let workstation trust extend to signing systems.
- Inventory every non-human identity, especially internal AI agents, and scope them like third parties.
- Build quorum, velocity limits, and circuit breakers into anything that moves money.
- Treat cyber hygiene as a founding-stage discipline, not an enterprise afterthought.
The attackers no longer breach walls. They befriend the people who hold the keys – and increasingly, the assistants who fetch them.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.