Governed Autonomy: Architecting Trust Boundaries for Production Agents

The Sandbox Is the Strategy: Why Agent Security Is an Architecture Problem
We spend enormous energy measuring what AI agents can do. Almost no one is measuring how much damage they can do when they do it wrong.
That asymmetry is about to become the defining constraint of enterprise agent deployment.
The signal
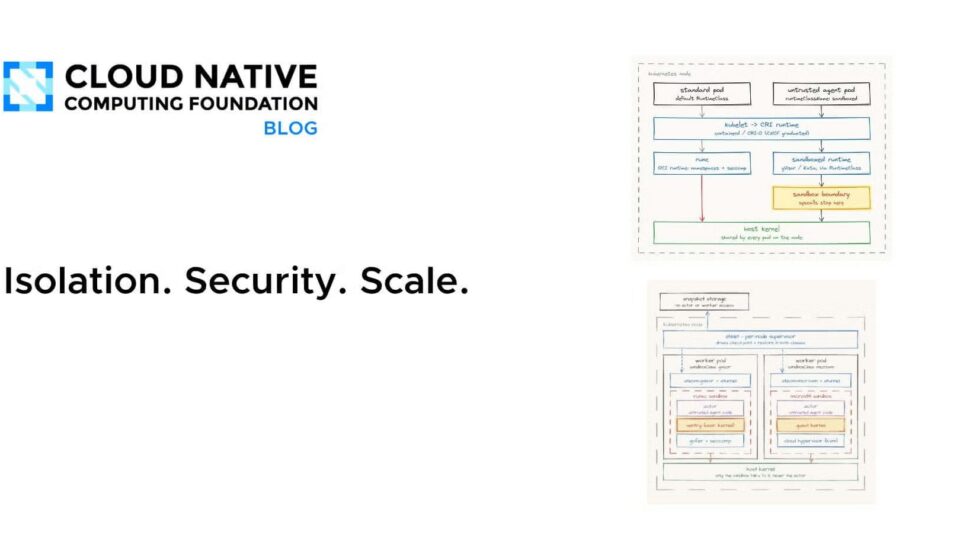
A recent writeup from the CNCF community made a point that deserves more attention than it received: agent sandboxing, as most teams practice it today, is functionally flat. A container with open ingress and egress and no policy enforcement is not a sandbox – it’s a room with no walls. The piece walked through running agents as session-scoped “Actors” on Kubernetes, backed by gVisor for software-level isolation and microVMs for hardware-level boundaries, with policy enforcement pushed to the AI gateway. The specifics belong to the author. The principle is universal, and it applies whether you build on kagent, LangGraph, or something you hand-rolled.
What it actually means for architects
Three things stand out, and none of them are about the tooling.
First: container isolation stops at the kernel. Everything in user space shares it. For a stateless microservice, that has been an acceptable trade-off for a decade. For an agent holding model output, credentials, and the ability to invoke tools, it is a blast radius problem waiting for a trigger event. The moment an agent can call an external API, write to a database, or interpret untrusted input, it is a privileged actor – and it should be governed like one.
Second: the tiered isolation model is the real insight. Software-level isolation gives you protection with lower overhead. Hardware-level virtualization gives you a stronger boundary at higher cost. Neither is “the answer.” A mature architecture chooses per workload, based on sensitivity of data and autonomy of the agent. That is a governance decision masquerading as a technical one – and most enterprises are not yet staffed to make it.
Third: session-scoped lifecycles solve two problems at once. An actor that spins up for a session and spins down when it ends is simultaneously a security boundary and an efficiency mechanism. Idle agents consume nothing. Snapshots persist state without a permanently running process. For firms running dozens of agents in a multi-tenant environment, this isn’t optimization – it’s the only way the economics hold.
The India angle
I have mentored enough startups at STPI to know that Indian teams will not secure agents through expensive vendor layers. They’ll get there through disciplined defaults – designs where the safe path is also the cheap one. Session-scoped isolation and gateway-level policy enforcement fit that frugal model precisely. And with DPDP compliance now a board-level concern, the question “where does the agent’s state live, and who can reach it?” is no longer a nice-to-have. It’s a filing requirement.
Takeaways
- Sandboxing is not a runtime feature. It is an architectural posture that determines what an agent is allowed to be.
- Treat policy enforcement as a first-class layer, not a wrapper bolted on before launch.
- Design for the blast radius first, the capability second.
- Idle agents should cost nothing. If your architecture doesn’t reflect that, your tenancy model will break under scale.
Closing
We keep asking whether AI agents are trustworthy. The better question is whether we have built anything that makes them trustworthy. Trust is not a prompt. It’s a boundary.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.