The Approval Stack: Why India’s Satellite Internet Race Runs Through Security

The Satcom Fight Isn’t a Queue. It’s a Pipeline – And Everyone’s Reading It Wrong.
We love a clean villain narrative. Billionaire vs. billionaire, crony capitalism vs. foreign arrogance. But having followed India’s digital infrastructure story for two decades, I’d argue the loudest assumption in this entire feud is also the most wrong: that satellite internet approvals are a single queue where someone is “cutting the line.” They aren’t. And the confusion is doing real damage to how we think about infrastructure governance.
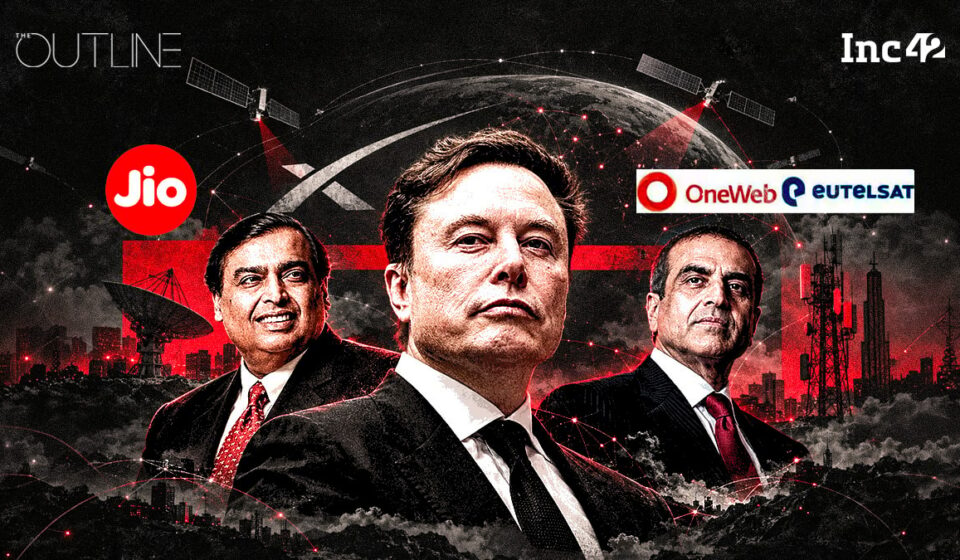
Here’s the signal beneath the noise: Elon Musk publicly accused Reliance of engineering a satcom monopoly and questioned why Starlink, after five years of compliance, still holds no licence. The Department of Communications countered that Starlink, Jio and Eutelsat OneWeb are at “broadly the same regulatory stage.” And critically – no satellite broadband service has actually launched in India. Anywhere. The fight is entirely about a queue that hasn’t moved for anyone yet.
Four Gates, Not One Queue
The approval process is not one event. It is four sequential gates: a GMPCS licence, an IN-SPACe authorisation, a security assessment, and spectrum assignment. Any architect will recognise this shape instantly – it’s a deployment pipeline. A GMPCS licence is passing code review. Spectrum assignment is the production deploy. Conflating all four into a single “approval” is exactly what makes the narrative so combustible, because it lets a claim of readiness masquerade as a claim of clearance.
And that distinction matters enormously. Starlink’s statement about building “dedicated gateways in-country” is a claim about preparation – feature-complete, in software terms. The security assessment is something else entirely: it is a verification of the control plane. Who can activate terminals? Who can reroute traffic, change coverage, or suspend service mid-conflict? Starlink’s role in Ukraine demonstrated that a foreign operator’s kill switch is not a hypothetical risk – it is geopolitical infrastructure. No sovereign state hands over that control surface without an audit, and no audit of that gravity should be judged by the impatience of a tweet.
Notably, the reported timelines cut against the monopoly theory: OneWeb completed its security demonstration before Starlink did, and applied five years ago. If anything, OneWeb is ahead in line – just quietly, without the theatrics.
The Structural Tension Nobody Names
The more interesting conflict is structural: Jio’s own IPO papers admit satellite broadband threatens JioFiber and AirFiber. The incumbent is simultaneously a competitor and a witness to the rules governing that competition. In such markets, the only genuine leveler is process transparency – documented criteria, a named authority for each decision, and a defined next step per applicant. In other words, regulators should run approval pipelines the way we run build pipelines: visible stage, owner, and exit criteria for every participant. Predictability is not the absence of rigor; it is rigor made legible.
The Bharat Angle – And Why It Raises the Stakes
For those of us building technology in Northeast India, satellite broadband is not a gadget story. It is the plausible last mile for health centres in river-valley districts, schools on ridgelines, and border outposts where fibre economics simply collapse. But that is precisely why the sovereignty checks matter more here, not less – border-region connectivity routed through a foreign-controlled constellation is a sovereignty question before it is a business question.
Strategic Takeaways
- Decompose governance. Name every gate, owner, and exit criterion. Monolithic “approvals” breed conspiracy; legible pipelines breed trust.
- Readiness ≠ clearance. Capability claims and control verification are different milestones. Leaders should stop collapsing them.
- Architect for the audit. Founders entering regulated infrastructure: design lawful interception, data localisation, and incident reporting into the system from day one. In regulated markets, compliance-by-design is the product.
The deeper lesson for every builder watching this circus: in critical infrastructure, trust is never granted at the launchpad.
It is earned through the audit trail.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.