Architecting Responsible Counter-Drone Systems for Mass Events

We treat rogue drones as a tactical nuisance – and that’s the problem. Framing counter-drone activity as a series of ad-hoc tactics for a single event misses the deeper architectural questions: how do you design resilient, lawful, and reusable airspace situational awareness for the long term?
Context (brief)
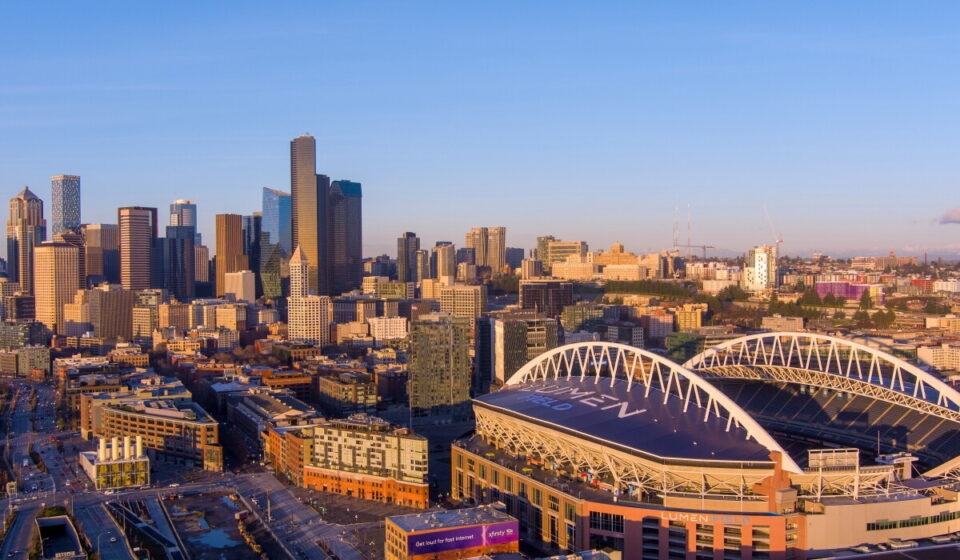
King County Sheriff’s Office is deploying commercial counter-UAS technology and its own drones around stadium matches during the upcoming FIFA World Cup, operating under Temporary Flight Restrictions and a federal grant that allows the agency to retain equipment after the tournament. The move pairs sensor-equipped mobile detection units with law-enforcement drone assets to improve situational awareness and operator engagement.
Why this matters beyond the stadium
At scale, protecting a temporary event from small unmanned aircraft systems exposes a systemic set of challenges that CTOs, architects and public-safety leaders should be thinking about now:
-
Sensor fusion and edge-first processing: Detecting and classifying small drones reliably in dense urban radio/noise environments requires multiple sensing modalities – radar, RF fingerprinting, electro-optical/IR imaging – combined at the edge. Centralized cloud analysis introduces dangerous latency; decisions about interdiction or evidence capture need sub-second confidence. Architectures must therefore prioritise low-latency pipelines, local model inference, and verifiable audit logs.
-
Interoperability, not vendor lock-in: Commercial counter-UAS systems vary in sensors, data formats and APIs. Procurement driven by a single event risk creates long-term vendor lock-in and brittle integrations. Public agencies should require open interfaces, standardized telemetry formats, and the ability to ingest feeds into broader command-and-control and air-traffic management systems.
-
Legal, ethical and operational guardrails: Technical capability (e.g., detection, RF locating, operator attribution) outpaces legal permission for interdiction. Civil liberties, evidence chain-of-custody, and rules of engagement must be designed in tandem with the tech stack. Expect friction between “detect” and “disrupt” – jurisdictions may be able to detect but not legally intervene without clear statutory authority.
-
False positives and adversarial resilience: Birds, kites, and hobby radios create abundant noise. Machine learning classifiers must be engineered for precision under adversarial conditions (e.g., spoofing, RF masking). Continuous monitoring, model retraining, and adversarial testing become operational necessities – not optional R&D projects.
-
Cost, reuse and capability permanence: The use of a federal grant to retain equipment after an event is a strategic win; it turns a short-term deployment into sustained capability. However, agencies need a roadmap for lifecycle costs – maintenance, training, software updates – and an architecture that allows redeploying assets across mission types (search-and-rescue, disaster response, critical infrastructure monitoring) to justify ongoing expenditure.
Relevance for India and regional planners
The architectural lessons translate directly to large public events across India – from international sporting fixtures to mass religious gatherings. Indian public-safety agencies and municipal bodies will face similar constraints: congested RF environments, opaque operator attribution, and the need to balance public safety with privacy. This is an opportunity for frugal, interoperable architectures: deployable sensor nodes with local inference, open-data exchange between civil aviation, police and municipal transport, and procurement policies that insist on standards rather than one-off bundles.
Actionable takeaways for architects and leaders
- Design for edge-first detection with layered sensor fusion to minimize latency and false positives.
- Insist on open APIs and exportable data formats in procurement to avoid long-term lock-in.
- Develop joint legal-technical playbooks before events: detection → attribution → authorized response.
- Plan for lifecycle: include software, threat-model testing, and operator training in total-cost calculations.
- Treat retained capability as a cross-mission asset; map reuse scenarios to justify capital spend.
Closing thought
Events accelerate capability acquisition – but if we treat every deployment as disposable, we pay with silos, outdated gear, and missed opportunities to build resilient, interoperable public-safety infrastructure. The smarter path is to design for persistence: architectures that respect law and privacy, scale across missions, and evolve with adversaries rather than chase them.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.