
Ten years ago, data residency was strictly a software, storage, and cloud-routing conversation. If an enterprise wanted absolute control, you bought the servers, racked them in a private data center, cut the external network cords, and called it sovereign. Today, geopolitics is descending all the way down to bare metal, challenging that fundamental assumption.
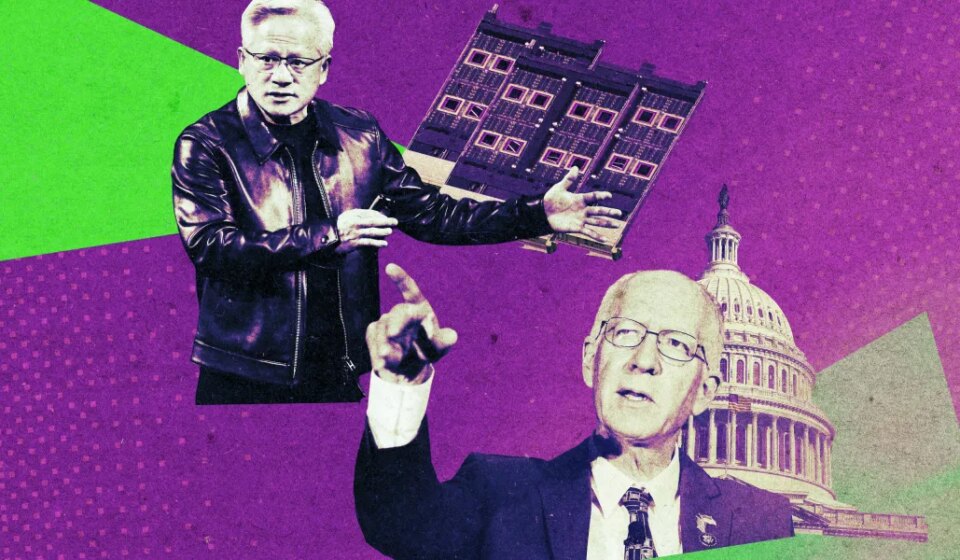
Recent policy debates surrounding proposed semiconductor security mandates in the US have exposed a fascinating divide between public lobbying and technical reality. While industry associations publicly argue that tracking the physical location of advanced AI chips is untested and potentially infeasible, chipmakers have privately acknowledged to lawmakers that the capability already exists. Through modern data center management telemetry, hardware vendors can already infer the geographic footprint of their compute fleets-leading regulators to push for mandatory, “ping-based” location verification embedded directly into advanced GPUs to curb cross-border smuggling.
The Erosion of Agnostic Silicon
Looking past the geopolitical friction, the core architectural signal here is profound: we are witnessing the transition from passive, agnostic hardware to active, tethered silicon.
For decades, enterprise software architects operated on a clear separation of concerns. Hardware provided raw compute; the operating system and orchestration layers managed network visibility. Implementing a mandatory ping-based mechanism-where a processor must signal its geographic coordinates upon coming online-fundamentally alters system design.
From a Chief Architect’s perspective, this introduces complex trade-offs between regulatory compliance and cyber resilience:
- The Air-Gap Paradox: High-security enterprises, defense networks, and critical financial infrastructures rely on strictly air-gapped topologies. Requiring advanced AI accelerators to phone home-or rely on periodic cryptographic location attestations-creates a massive architectural contradiction. How do you maintain a zero-egress environment when your silicon demands external validation?
- New Attack Surfaces: Every mandatory telemetry channel is a potential vulnerability. If a chip can be tracked or potentially throttled remotely to prevent illicit diversion, that same mechanism becomes a prime target for bad actors looking to spoof location data or trigger denial-of-service events at the firmware level.
- Latency and Operational Tech Debt: Embedding geopolitical compliance into hardware roots-of-trust adds a layer of brittle dependencies. If an attestation server faces an outage or a diplomatic policy shifts overnight, legitimate enterprise workloads could face unexpected operational friction.
Why Compute Sovereignty Matters for Bharat
In my discussions within state technology committees and academic boards here in India, the conversation around AI governance rightly focuses on data localization and indigenous foundational models. However, this emerging trend in hardware telemetry highlights a blind spot: data sovereignty is incomplete without compute sovereignty.
As India scales its Digital Public Infrastructure (DPI) and accelerates national AI initiatives to solve last-mile challenges in healthcare, agriculture, and governance, our reliance on imported, black-box silicon presents a long-term strategic vulnerability. If the foundational compute powering a nation’s public digital stack is subject to foreign firmware mandates and remote location tracking, true architectural autonomy remains elusive.
For the young engineers and deep-tech founders I mentor, this is a massive wake-up call. The future of resilient tech isn’t just about writing clever wrappers around existing LLMs; it lies in going deeper down the stack. Investing R&D into open-standard architectures like RISC-V, building verifiable firmware, and developing indigenous semiconductor packaging are no longer academic exercises-they are national and enterprise imperatives.
Strategic Priorities for Tech Leaders
As hardware becomes increasingly entangled in global supply chain policing, CTOs and Enterprise Architects must adapt their long-term roadmaps:
- Audit Hardware Dependencies: Treat firmware and hardware-level management engines with the same Zero-Trust scrutiny applied to third-party SaaS APIs. Understand exactly what telemetry your bare-metal infrastructure emits.
- Architect for Compute Agnosticism: Avoid locking AI pipelines into a single vendor’s proprietary hardware ecosystem. Design cloud-native and on-premise workloads using abstraction layers that allow portability across diverse accelerators.
- Factor Geopolitics into Disaster Recovery: Business continuity planning must now account for regulatory supply-chain shocks and firmware-level compliance shifts, not just fiber cuts and server failures.
For thirty years, the tech industry romanticized the idea of a borderless cyberspace. We are now learning a hard truth: while code may still cross borders effortlessly, the silicon it runs on is rapidly being issued a passport.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.