Who Owns the Agentic Web? Amazon’s Block on Meta Signals the Next Platform War

The Web Is Not Ready for Autonomous Agents-and Identity Alone Will Not Fix It
An AI assistant that understands what we want is only half the capability. The more consequential question is whether a website should trust it to act on our behalf.
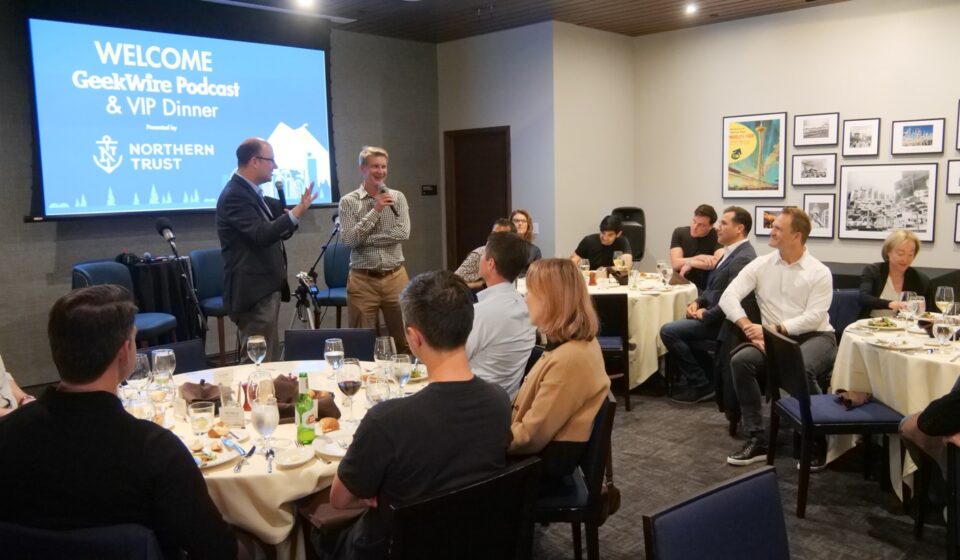
A recent GeekWire podcast discussion highlighted an early confrontation between Amazon and Meta’s Muse AI assistant. Amazon is reportedly blocking the agent from shopping because it does not identify itself and violates the platform’s conditions of use. Although framed as a dispute between two technology companies, this is a much larger signal: enterprises are moving toward a world where software will browse websites, negotiate with services, compare options, and initiate transactions-not merely generate recommendations.
The real issue therefore goes beyond whether an agent should disclose that it is a bot. It concerns the absence of a robust architecture for delegated digital action.
Authentication Is Not Permission
Modern web systems already have mechanisms for answering “Who is this?” API keys, OAuth tokens, user accounts and identity providers can authenticate software and its users.
But authenticated action is not the same as authorized action.
When a person delegates a task to an AI agent, several distinct questions arise:
- Identity: Who is the agent?
- Authority: Is it permitted to act for this user?
- Consent: Did the user knowingly delegate this specific task?
- Limits: How much can it spend, share, publish, or irreversibly change?
- Liability: Who is responsible when the outcome differs from the user’s intent?
A valid login token may establish that an application has access. Yet it rarely captures the purpose, constraints, duration, or risk tolerance of a particular instruction. Traditional access-control systems were designed around roles and resources, not dynamic, intent-based delegation.
This is a significant architectural gap.
The Enterprise Must Make Delegation Machine-Readable
From an enterprise architecture perspective, AI agents should be treated as new digital actors-not simply larger users with better language skills.
An agentic workflow will require structured records for delegation, intent, consent, and authorization. A transaction envelope should identify the human principal, the agent, the permitted purpose, approved limits, expiry time, and revocation status. It should also preserve evidence of what instructions the user gave and what actions the agent took.
These controls cannot rely only on a terms-of-use page or a final “Are you sure?” dialog. Human confirmation becomes superficial when an agent is negotiating across multiple services and the user cannot reasonably evaluate every consequence.
High-risk actions-financial transfers, contract acceptance, healthcare decisions, production infrastructure changes, or publication of sensitive information-need risk-based controls, scoped permissions, transaction ceilings, expiration periods, and meaningful human checkpoints. Every action must also generate an auditable event.
For CIOs and CTOs, this means agent governance cannot be bolted on after deployment. Consent management, policy decision points, identity services, observability, and legacy authorization models must evolve together.
From Static Terms to Dynamic Trust
Websites are still primarily designed for human-operated browsers, while APIs created a partial machine-to-machine layer. Agentic AI now introduces a more difficult pattern: autonomous software negotiating with autonomous services on behalf of people.
Terms written for legal accountability are not necessarily understandable or enforceable in real time. Platforms will increasingly need to expose machine-readable capabilities and restrictions-what agents may access, what information they may use, and which actions require additional authorization.
The deeper question is not whether agents should be allowed to shop, book, or negotiate. It is whether digital ecosystems are prepared to distinguish helpful autonomy from uncontrolled agency.
There is also a relevant parallel in India’s digital public infrastructure. UPI and Aadhaar demonstrate the value of interoperable, large-scale digital rails. But agentic systems require an additional layer: verifiable, purpose-bound delegation. Consent should be specific, revocable and auditable; identity verification should never be mistaken for authorization to act.
Key Takeaways
- Treat every AI agent as a distinct digital identity with explicitly scoped authority.
- Record consent and delegation as machine-readable, time-bound and revocable data.
- Design irreversible actions for risk-based approval, not blanket access.
- Modernize legacy access controls to support purpose, limits, expiry and full auditability.
- Require machine-readable platform policies while preserving clear human-readable terms.
The next major web-platform shift will not be measured by how intelligently agents can browse, but by how responsibly they can act.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.