Commodifying Wildlife: Regulatory Blindspots and Corporate Risk

The cost of “move fast and scale” when you don’t know the domain
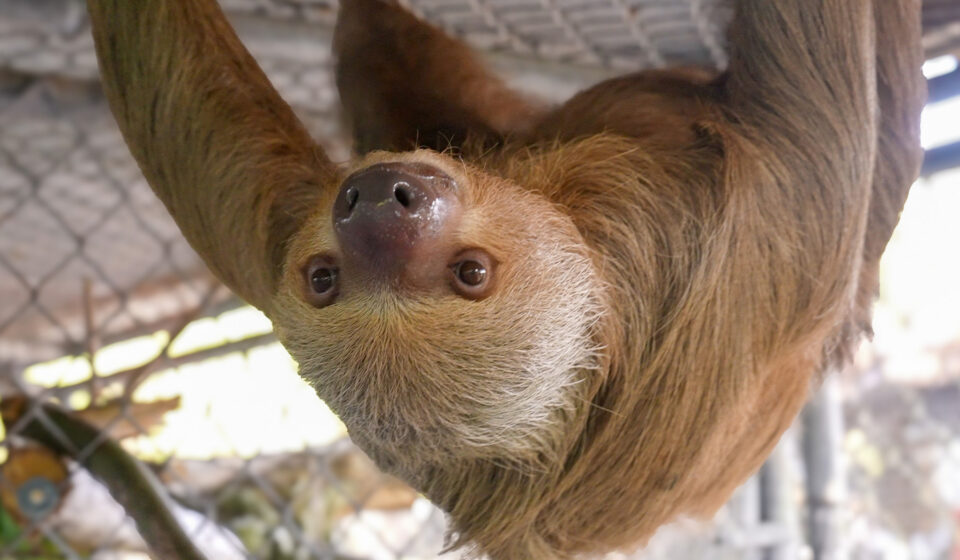
The image that sticks with me from the recent Sloth World story is not a regulatory memo or a news headline – it’s a living creature whose specialized biology was treated like an interchangeable asset. That human-made mismatch between business velocity and domain knowledge is a lesson every architect and technology leader should read as a warning.
What happened (in brief)
I recently read investigative coverage showing that a commercial sloth operation in Florida imported dozens of wild animals, expanded rapidly, and suffered catastrophic animal losses. Local investigators found poor conditions, inexperienced clinical care, and operational shortcuts – yet concluded criminal statutes were not met because the law’s definitions and enforcement mechanisms were narrow. The tragedy therefore exposed gaps in oversight, expertise, and accountability rather than a single technical failure.
Why this matters to architects and CTOs
Treat this as a systems-design failure, not merely an ethical one. Enterprises and platforms scale in similar ways: initial idea → rapid onboarding → operational complexity → stress on marginal capabilities → emergent failures. The Sloth World case highlights several architectural anti-patterns that are common in tech organizations:
-
Weak observability: Decision-makers relied on spot inspections and self-reported records rather than continuous, objective telemetry. In software systems we instrument extensively; in physical or regulated operations we too often accept opaque human reports and sparse audits. The absence of timely, machine-verifiable signals allows bad outcomes to accelerate.
-
Domain-expert deficit: Hiring clinicians without sloth experience is analogous to deploying ML models in a high-stakes domain without domain experts in the loop. Scaling any sensitive capability without relevant expertise introduces brittle operational decisions and inappropriate remedies (e.g., “overmedicating” or overfitting).
-
Incentives that reward growth over resilience: Volume-driven KPIs (how many animals imported, how many visitors expected) can override health-and-safety constraints. In tech, growth metrics can similarly mute risk signals until they become crises.
-
Regulatory blind spots = architectural debt: Laws and enforcement that are narrowly framed create “black holes” where harm can occur without legal consequence. For systems architects, regulatory ambiguity is a form of external technical debt you must anticipate and design against.
Actionable guidance for leaders
-
Build observability around outcomes, not just processes: Define clear, measurable outcome metrics (mortality, welfare indicators, error rates) and instrument them. Use anomaly detection to flag facilities or services deviating from safe baselines.
-
Require domain credentials and continuous CPD: For any regulated or sensitive domain, make domain experts non-negotiable in governance, not optional consultants. Their presence should be codified in operating procedures and escalation paths.
-
Adopt gradual, measurable rollouts: “Canary” deployments aren’t just for code. Incremental scale-up with predefined health gates forces teams to prove operational maturity before volume grows.
-
Independent third-party audits and provenance: Independent certifiers and tamper-evident records (supply-chain provenance) reduce single-point self-reporting failures. Transparency aligns incentives and enables faster enforcement or remediation.
-
Design legal-technical interfaces: Where laws are vague, design contracts, SLAs and internal policies that translate legal intent into enforceable technical checks – e.g., mandatory telemetry submission, public dashboards for key welfare metrics, or automated compliance reports.
A note for India and similar jurisdictions
While wildlife and enforcement contexts differ regionally, the core architecture lessons hold: opaque supply chains, narrow enforcement definitions, and rapid private-sector scaling are global risks. In India, where wildlife protection and last-mile enforcement already face resource constraints, digital tools for provenance, outcome telemetry and stronger domain oversight can be part of the solution – but only when coupled with policy clarity and community capacity building.
Takeaways
- Never substitute domain expertise with process workarounds.
- Instrument outcomes and make them auditable.
- Scale only behind explicit health gates and independent verification.
- Treat regulatory ambiguity as technical debt and mitigate it proactively.
Closing thought
Systems – whether digital platforms or animal-care operations – reflect the priorities we encode. If safety and stewardship aren’t first-class design constraints, scale will expose the moral and technical debt we chose to ignore.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.