From Centralized IT to Enterprise Value: The Next State Technology Imperative

Centralized Government IT Has Entered Its Harder Phase
The hardest part of centralizing government technology is not moving staff, servers, and applications under one roof. It is deciding what that “one roof” should standardize-and what must remain close to the departments that understand the work and the data.
Many consolidation programmes mistake organizational centralization for architectural maturity. That is where the real difficulty begins.
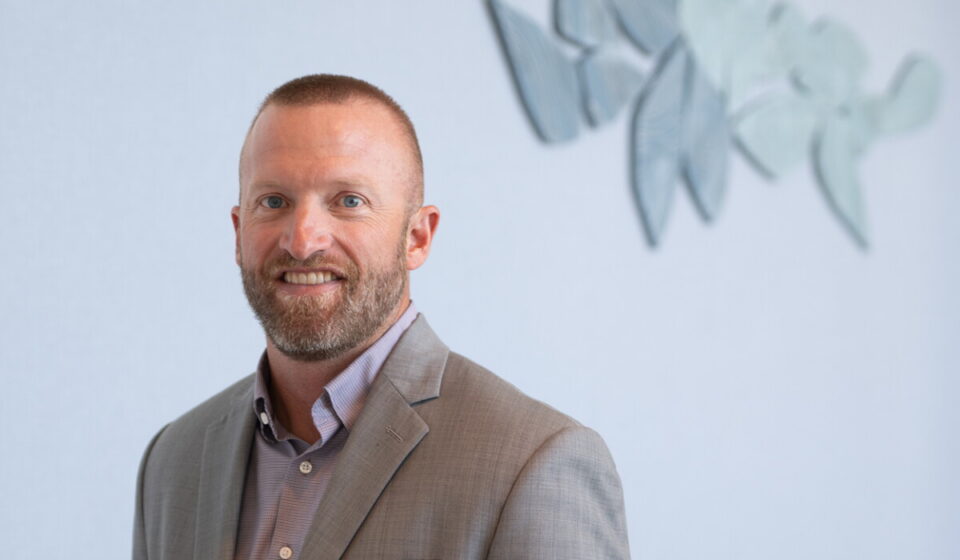
A recent profile of Idaho’s interim state CIO, Jake Reynolds, makes this tension visible. Since completing the move of agency technology staff into a centralized IT organization in 2022, Idaho is shifting from the logistics of consolidation to proving daily value-while addressing technical debt, delayed cloud modernization, and AI ambitions constrained by incomplete data classification.
Centralization Is an Operating Model, Not a Destination
Reynolds’ use of agency relationship managers and embedded liaisons is more than a communications tactic. In a sociotechnical system, relationships are part of the architecture.
If ownership and escalation paths are unclear, even a technically sound platform can be perceived as an adversary. If requests are slow, departments route around IT rather than through it.
The better model is federated. Identity, cybersecurity, cloud guardrails, observability, and service management can be standardized. Workflows, data meaning, and operational priorities should remain close to the departments that own them. One roof should not necessarily produce one rigid hierarchy.
If an architecture diagram does not show who owns decisions, resolves conflicts, and protects service quality, it is incomplete.
Modernization Must Follow Value, Not Fashion
Cloud modernization remaining on Idaho’s strategic agenda for years without becoming a strong execution programme is a familiar warning. Strategy often remains aspiration when organizations ignore architectural dependencies and funding realities.
Moving inherited websites and technical debt into a cloud environment does not remove that debt; it can sometimes make it harder to see. Cloud is an operating model, not a destination, and “lift and shift” should not be mistaken for transformation.
I would sequence modernization using four lenses: business value, risk reduction, technical dependencies, and organizational readiness. Every wave needs an accountable owner, measurable outcome, and exit criterion.
A low-value website may still be a significant security concern. A critical identity service may lack documentation or tested recovery. Modernization means making such trade-offs explicit rather than migrating everything indiscriminately.
AI Readiness Is Data Governance in Disguise
The deeper lesson from Idaho is that AI cannot be scaled responsibly until agencies understand and classify their data.
Central IT can provide models, platforms, security controls, and governance capabilities. But business owners must explain what the data means, why it may be used, who may access it, and which decisions must never be automated. Without that semantic context, an apparently efficient model can produce unreliable, discriminatory, or legally exposed outcomes.
The answer is not to wait for a perfect governance framework. It is to create controlled, reusable patterns: approved use cases, risk tiers, evaluation datasets, human escalation, logging, and audit trails.
Early implementations should be narrow, measurable, and reversible. Success should be judged by service quality and public value-not by the number of pilots launched. Most importantly, every pilot should produce reusable controls rather than another isolated experiment.
A Lesson for India’s Digital Public Infrastructure
There is a useful parallel with India’s Digital Public Infrastructure. Shared rails-identity, payments, data exchange, and trust-can support many services, while sectoral institutions retain responsibility for local workflows and sensitive domain data.
State digital programmes should follow the same principle. Central platforms can provide standards-based APIs, security, observability, and grievance mechanisms; departments remain accountable for data quality and citizen outcomes.
In Northeast India, where connectivity and administrative capacity vary considerably, digital architecture must also support assisted channels and graceful degradation rather than assume every interaction is smartphone-first.
Key Strategic Takeaways
Consolidation’s completion marks the beginning of proving value. Value must be measured through reliability, responsiveness, and better public services. Furthermore, relationship ownership is a critical architectural component. Modernization should proceed in risk- and value-based waves, avoiding indiscriminate cloud migration. AI pilots must also produce reusable governance mechanisms instead of isolated experiments.
The next phase of government technology will be won not by organizations that centralize the most, but by those that connect technology, governance, and institutional trust effectively.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.