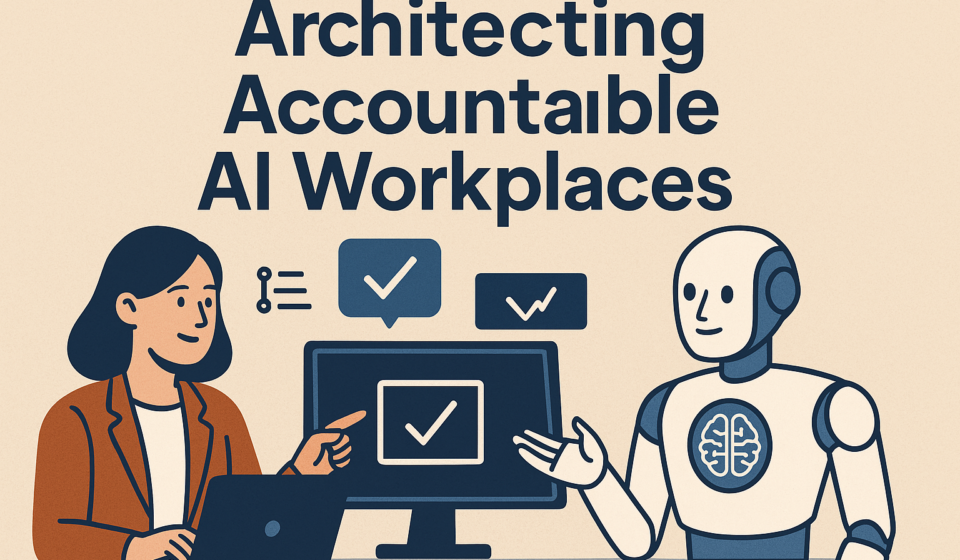

We often celebrate the two-hour-a-day productivity dividend AI promises – and then quietly ignore the governance debt that grows with every unchecked prompt. The real bottleneck today isn’t model performance; it’s organisational trust: who owns the output, who is accountable when it fails, and how do systems make that traceable?
A new global study released on 15 September 2026 by GoTo and Workplace Intelligence surveyed 2,500 employees and IT leaders and found a sharp dichotomy: employees see clear efficiency gains from AI, yet most fear blame for AI mistakes and many avoid using these tools or use them without adequate checks. Small businesses, in particular, are lagging on policy and training – a recipe for both missed value and hidden risk.
What this means for enterprise architecture and senior leaders
The study’s numbers are a wake-up call for architects and CTOs: accelerating AI adoption without concurrent investments in governance, observability and human-centred design amplifies systemic risk. From an architectural standpoint, there are three immediate shifts we must plan for.
-
Treat AI as a composite service, not a black box.
Design AI features the same way you design payment or identity systems: with layered contracts, SLAs, and observability. That means model registries, versioned deployments, deterministic test harnesses and provenance metadata attached to every output. Build API gateways that enforce usage policies, and instrument every request/response for audit. -
Operationalise human-in-the-loop, not just for edge cases.
Human review cannot be an afterthought. For high‑stakes tasks – legal, financial, safety-critical decisions – default to explicit human approval workflows, confidence thresholds, and fallbacks. Architect workflows so that humans can easily inspect the provenance of a suggestion, rerun it with constrained prompts, or escalate without punishing individuals for raising concerns. -
Move from ad-hoc checks to continuous model risk management.
Shift left: integrate model testing into CI/CD (unit tests, adversarial tests, safety tests) and monitor drift, latency spikes, and unusual failure modes in production. Establish a cross-functional model-risk register (business impact, data lineage, privacy exposure) and tie it to incident playbooks and insurance where appropriate.
Trade-offs: speed vs. stability, and decentralisation vs. control
Many organisations are tempted to favour rapid rollout and local autonomy – “let teams experiment with their own AI tools.” That accelerates innovation, but increases the likelihood of inconsistent guardrails, data leakage and accountability gaps. The pragmatic balance is a federated model: central guardrails (policy, logging, model inventory) with local product ownership and measured autonomy (sandboxed experiments, canary releases). This preserves velocity while containing systemic risk.
Why small organisations and emerging ecosystems must care
The study’s observation that only a minority of small organisations have AI policies resonates deeply with what I see in the field. MSMEs in India – including many in the Northeast – rarely have the legal, security or engineering bandwidth to build model governance from scratch. But they have something powerful: community networks and shared platforms (DPI-like services, industry clusters, STPI incubators). Low-cost, shared guardrails – template AI policies, a common playbook for incident reporting, and regional model-vetting labs – can lower the barrier to responsible adoption.
Practical takeaways for CTOs, founders and board members
- Establish an AI policy baseline within 90 days: permitted use cases, prohibited uses, review thresholds, and an incident escalation path.
- Create a model registry and require metadata (version, training data pedigree, expected failure modes) before production.
- Instrument for provenance and auditing: every AI output used in business decisions must be traceable to a model/version and input.
- Implement “shadow mode” rollouts and human-in-the-loop for high-risk flows; measure real-world error rates before full release.
- Train staff on failure modes and create a non‑punitive reporting culture so mistakes surface early.
- For MSMEs: collaborate with local incubators or consortia to share compliance resources and low-cost testing facilities.
Closing thought
AI will repay organisations that pair speed with discipline; those that don’t will pay in lost trust, regulatory hassle and avoidable harm. The technical challenge is solvable – the cultural one will determine who captures the real value.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.