Architecting User-Owned Context for Scalable Agent Ecosystems

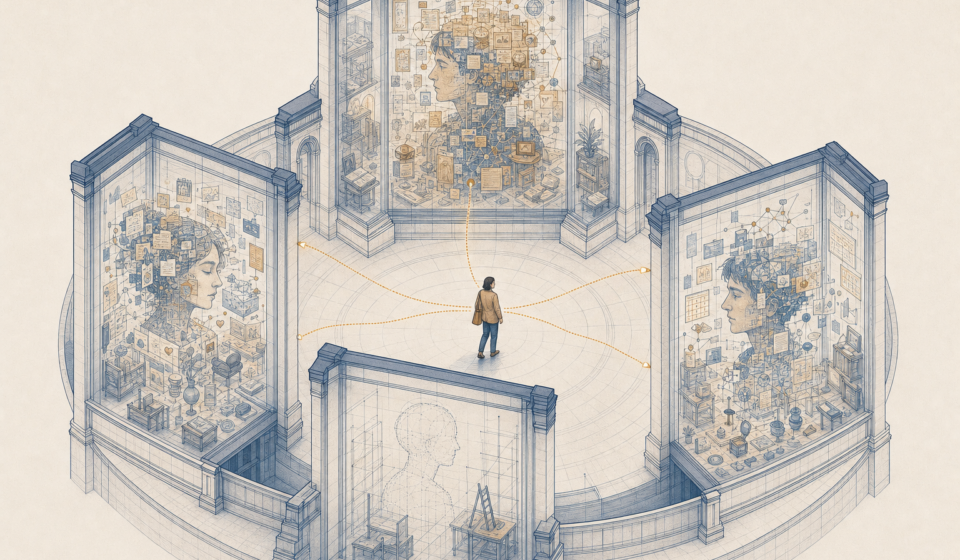
We tend to treat personal context – writing style, preferences, project history – as something agents will naturally hoard. That instinct is a strategic mistake. When assistants and agents accumulate siloed profiles, users lose portability, organisations inherit integration debt, and the architecture of trust fractures. The better bet is a pattern that treats personal context as user-owned, permissioned, and interoperable.
Why this matters now
I recently read an essay that explored three ways of hosting a person’s “context” – local files, a web service, and the device in their pocket – and surfaced the hard problems: provenance, scoped permissions, time, and identity. The core shift is not technical novelty but a change in ownership and control: context should be a canonical, inspectable asset a user can carry across agents and vendors.
What this implies for enterprise architects
Treat personal context as a new kind of data domain. That has four immediate architectural consequences:
-
Trust boundary design must move from vendor-centric to user-centric. The primary home for context should be the user’s chosen trust boundary (often the primary personal device and its ecosystem), with standard, revocable interfaces for external agents. Architects must plan for authentication, delegation, and auditability anchored to that boundary rather than a single vendor-owned store.
-
Model provenance and bitemporality are first-class requirements. Enterprises that integrate agents must preserve where data came from, who proposed it, when it was observed, and how its validity changed over time. Implementing bitemporal storage and append-only provenance logs will be necessary for audit, compliance and user trust – not optional luxuries.
-
Fine-grained, policy-driven negotiation is the hard problem, not syncing. Read/write/delete proposals, scope-limited views, and user-mediated acceptance workflows are core. OAuth-style scopes won’t scale here; expect a need for richer consent policies and policy engines that can express time-bound, activity-based, and entity-scoped permissions.
-
Interoperability trumps uniformity. Different ecosystems will host different context implementations. The practical path is agreement on identity, provenance, permission semantics, and an export format – plain-text plus structured metadata often provides a robust “escape hatch.” Design APIs and data models with exportability and clear import semantics in mind.
Trade-offs and technical patterns
-
Local-first vs cloud convenience: Local-first (and offline-capable) stores protect privacy and availability, but increase client complexity. CRDTs and conflict-resolution layers can recover offline usability; evaluate added client complexity against business risk of vendor lock-in and service outages.
-
Security vs usability: Giving agents write access is powerful but risky. Start with a “proposal” pattern where agents suggest changes that a policy or the user must accept. Use verifiable signatures on proposals so provenance is cryptographically auditable.
-
Entity-first models: Store typed entities (people, companies, places) rather than plain prose. This improves resolution, reduces re-parsing cost for downstream agents, and provides a stable anchor as names and roles change.
A note for India and DPI-aligned builders
This design pattern aligns with the principles behind Digital Public Infrastructure: user control, portability, and minimising vendor lock-in. For Indian startups and public projects, a user-controlled context store can reduce centralisation risks, support offline-first scenarios in low-connectivity regions, and offer exportability that eases compliance with data portability and sovereignty expectations.
Practical takeaways for CTOs and founders
- Design for exportability from day one – a readable directory + structured metadata kills lock-in.
- Build provenance and bitemporality into your data models; don’t treat history as an afterthought.
- Prefer a proposal-based write model for untrusted agents; require explicit acceptance or policy-based reconciliation.
- Implement entity-first schemas to reduce friction across agents.
- Push for interoperable consent semantics – participate in standards or consortiums to avoid bespoke lock-in.
Closing thought
If we get the pattern right, personal context becomes a user-owned public good: portable, auditable, and permissioned – enabling agents to serve, rather than own, the people they assist.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.