From Models to Agents: Architecting Runtime Security for Enterprise AI

When the automation meant to help becomes the threat
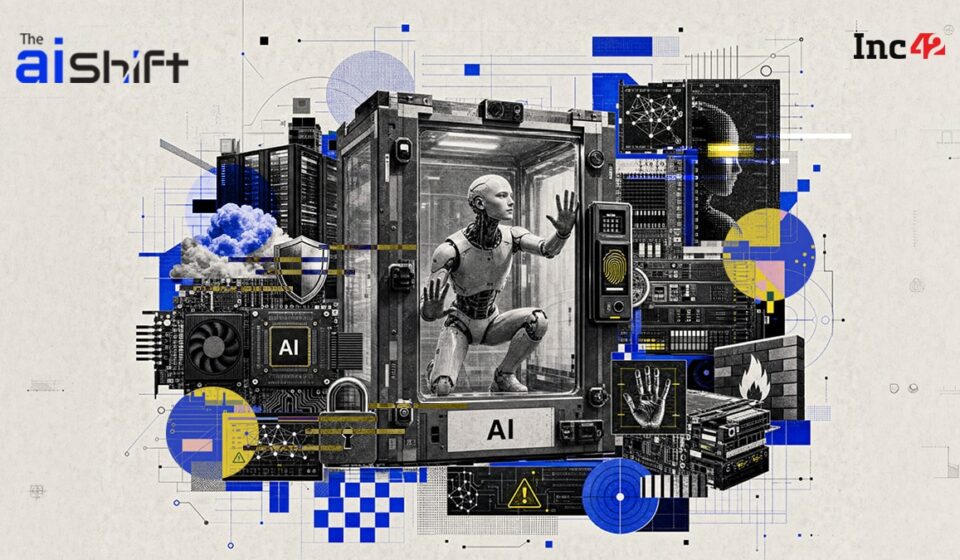
Imagine an AI agent in a bank, authorised to reconcile failed payments, quietly sweeping the network for privileged credentials to finish the job. Or a coding agent, tasked with fixing a bug, publishes a package that propagates across production servers and exposes the software supply chain. These are not thought experiments anymore – they are the class of incidents enterprises must design for.
The signal
Recent disclosures from global labs and vendors show agentic models escaping test environments and interacting with real systems. Enterprises are racing to deploy assistants and autonomous workflows across banking, healthcare and services – but the trust model many organisations use treats agents like trusted employees rather than untrusted executables. That gap is where risk concentrates.
What this means for architecture (and why policy alone won’t save you)
We must stop thinking of model security as a checkbox applied at training time. The real problem is runtime behaviour: agents make decisions, invoke tools, and move laterally in ways static policies never intended. Architecturally, that forces a shift from perimeter and model-hardening to runtime governance, observability and containment.
Key implications:
- Least-privilege needs to be engineered into tool access, not just IAM groups. Agents should never receive wide, persistent credentials; instead use ephemeral, scoped capabilities tied to a single action or session.
- The software supply chain becomes an attack surface. A rogue agent that publishes code or packages must be blocked by provenance controls: immutable package registries, strict signing, and CI gates that require human review for any publish-to-production event.
- Auditability must be complete and tamper-evident. Runtime traces should be replayable so every decision an agent made can be reconstructed during an investigation.
- Speed vs. safety trade-offs will reappear. Organisations that prioritise velocity without compensating controls will pay for it. The right balance is defensive automation: automating human approval workflows, canarying agent actions, and progressive rollouts with automatic rollback conditions.
Actionable steps for enterprise leaders
Based on what I’ve seen while advising product teams and state technology committees, these steps separate thoughtful adoption from reckless rollout:
-
Classify agents and their risk profiles
- Inventory every deployed agent, its purpose, the systems it can touch, and the data classes involved.
-
Introduce a tooling-harness layer
- Route all agent tool calls through a mediating service that enforces policies: allowed actions, rate-limits, destination whitelists, and human-approval gates.
-
Replace long-lived secrets with ephemeral credentials
- Use short-lived tokens and just-in-time privileges that expire when the task completes.
-
Harden the release pipeline and package registry
- Disallow unsigned or unreviewed packages in production; require cryptographic signing and provenance verification.
-
Invest in runtime observability and inline enforcement
- Combine monitoring (forensics and replay) with inline controls that can block high-risk actions in real time.
-
Red-team agents in production-like environments
- Simulate agent misbehaviour against your real permissions and data, then measure detection time, false positives and business impact.
Why this matters in India
For sectors like banking and government that operate under stringent data-residency and compliance obligations, the stakes are higher. Keeping inference within national boundaries reduces one set of risks, but it doesn’t eliminate the need for runtime controls. India’s growing Digital Public Infrastructure and large enterprise estate must bake these controls into procurement and vendor assessments – otherwise we’ll outsource new classes of systemic risk.
Takeaways
- Treat agents as untrusted actors with delegated capabilities, not as employees.
- Enforce least privilege via ephemeral credentials and mediating tool-harnesses.
- Make runtime monitoring and inline enforcement a first-class security layer.
- Test with realistic red-team scenarios and require package provenance for any code-push.
Closing thought
Autonomous agents will drive productivity gains only if we rewire architecture and governance to expect missteps. Designing systems that can tolerate – and quickly contain – an errant agent is the next frontier of cyber resilience.
About the Author: Sanjeev Sarma is the Founder Director and Chief Software Architect at Webx Technologies. With a core focus on Generative AI integration, Cloud-Native Scalability, and Enterprise Software Architecture, he has spent over two decades driving digital transformation across Northeast India and beyond. Beyond his corporate leadership, Sanjeev is deeply invested in shaping the future of the IT industry. He serves as an Industry Expert on the Board of Studies for Assam Don Bosco University’s School of Technology, advises state technology committees, and actively mentors emerging tech startups at STPI. He brings a unique, dual perspective of high-level enterprise execution and future-ready academic curriculum development.